
 Technology: Microsoft Purview
Finance: Insider Risk and Adaptive Protection at a financial institution
A financial institution makes security controls risk-driven with Insider Risk Management and Adaptive Protection, and ties communication oversight to a demonstrable audit trail.
Business challenge
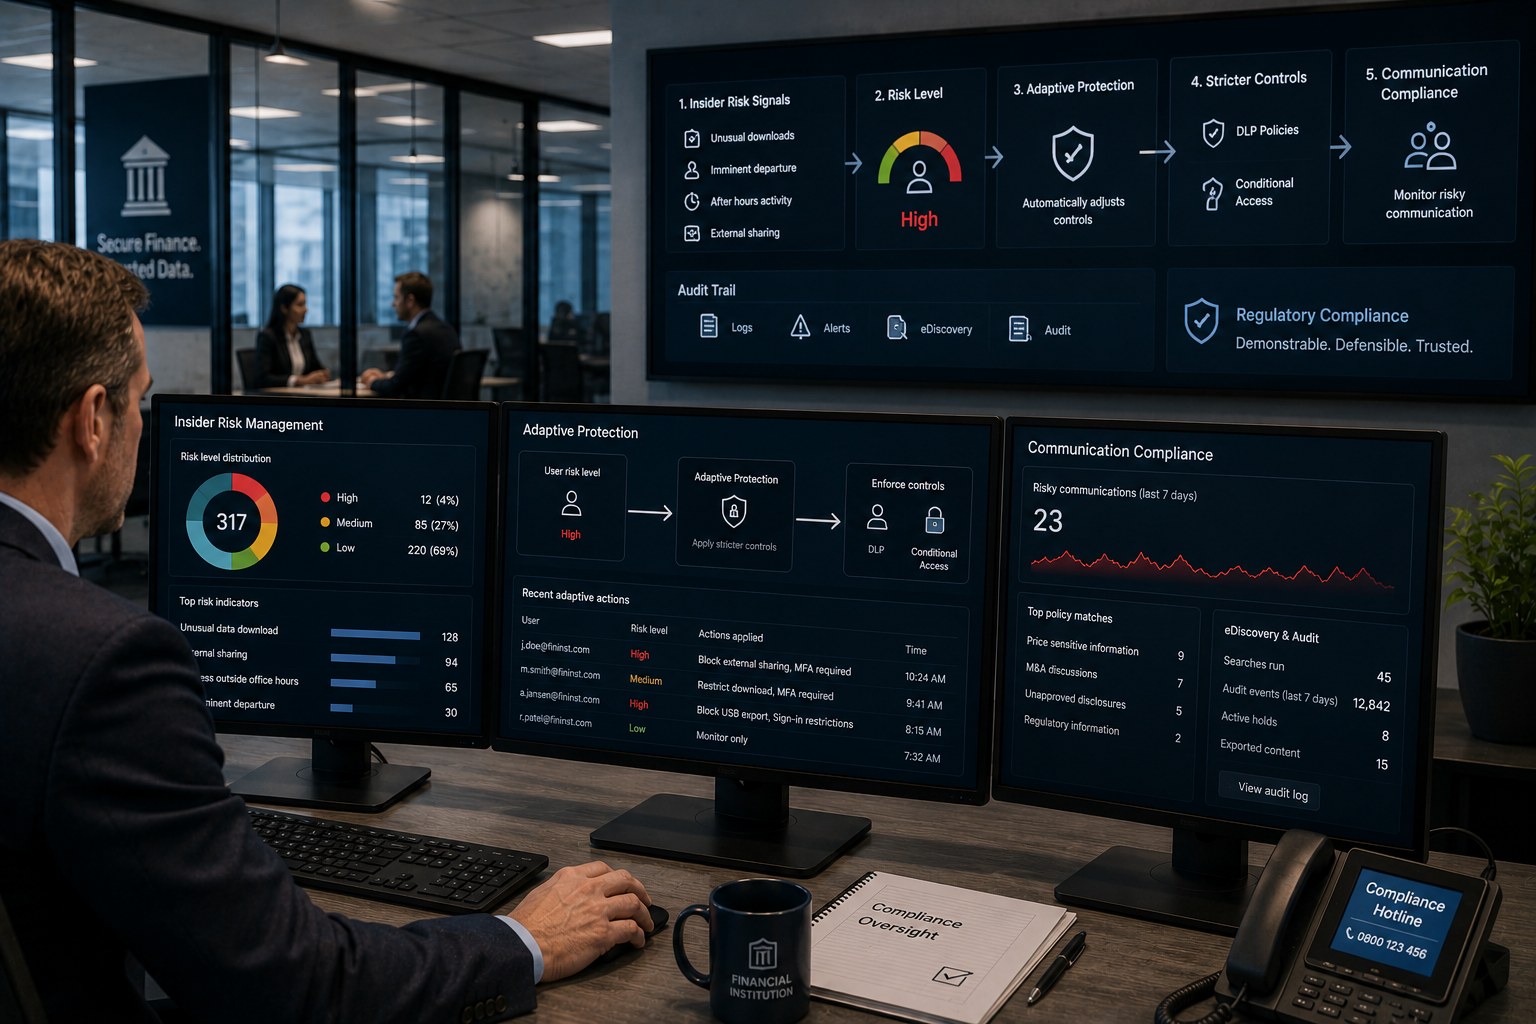
A regulated financial institution had to demonstrate that internal data leaks and market-sensitive communication were being watched, but existing policy was static: everyone got the same controls, regardless of risk profile. A handful of genuine risk cases drowned in thousands of generic alerts.
Architecture
Insider Risk Management gathers signals, such as unusual download patterns, an employee's impending departure, or activity outside office hours, and computes a risk level per user. Adaptive Protection automatically ties that risk level to stricter DLP rules and Conditional Access policy in Microsoft Entra ID, so controls tighten precisely for the users who need it. Communication Compliance watches risky communication patterns, for example around price-sensitive information, and eDiscovery and Audit record the whole for oversight.
Why this choice
Static, identical-for-everyone controls generated too much noise to be usable. A risk-driven model concentrates the compliance team's attention on the cases that actually matter, without touching the daily productivity of the vast majority.
Alternatives
Uniform DLP rules for the whole organization, without risk differentiation, were simpler to implement, but produced exactly the noise problem the institution wanted to solve. A fully manual communication oversight process was theoretically possible, but not scalable across thousands of employees.
Trade-offs
- Risk-driven controls need a careful privacy framework: employees must know that and why risk signals are collected.
- Adaptive Protection adds dependencies between Purview and Entra Conditional Access; changes to one policy can affect the other.
- Communication Compliance needs trained reviewers; without capacity for timely review, oversight loses its value.
Microsoft products
Microsoft Purview (Insider Risk Management, Adaptive Protection, Communication Compliance, eDiscovery, Audit), Microsoft Entra ID (Conditional Access).
Best practices
- Separate policy management (who sets rules) from investigation (who reviews signals), as an explicit separation of duties.
- Communicate transparently about which signals are collected and why, to maintain trust.
- Review risk thresholds periodically; a threshold that was correct on day one can become irrelevant after a reorganization.
Lessons learned
The first months turned out to be mostly a calibration exercise: the initial risk thresholds were too sensitive and again generated too many alerts. Only after two calibration rounds did volume drop to a level the compliance team could actually review.
Architecture at a glance
Click a component for details
Insider Risk signals
Unusual download patterns, an employee's departure, activity outside office hours.
Adaptive Protection tightens controls precisely for the users who need it, not for everyone.
Related content
Related how-tos
Related best practices