
 Technology: Microsoft Purview
Healthcare: protecting special category data with Microsoft Purview
A healthcare organization classifies and protects patient data with Data Map, sensitivity labels, DLP and Insider Risk Management, without slowing down care delivery.
Business challenge
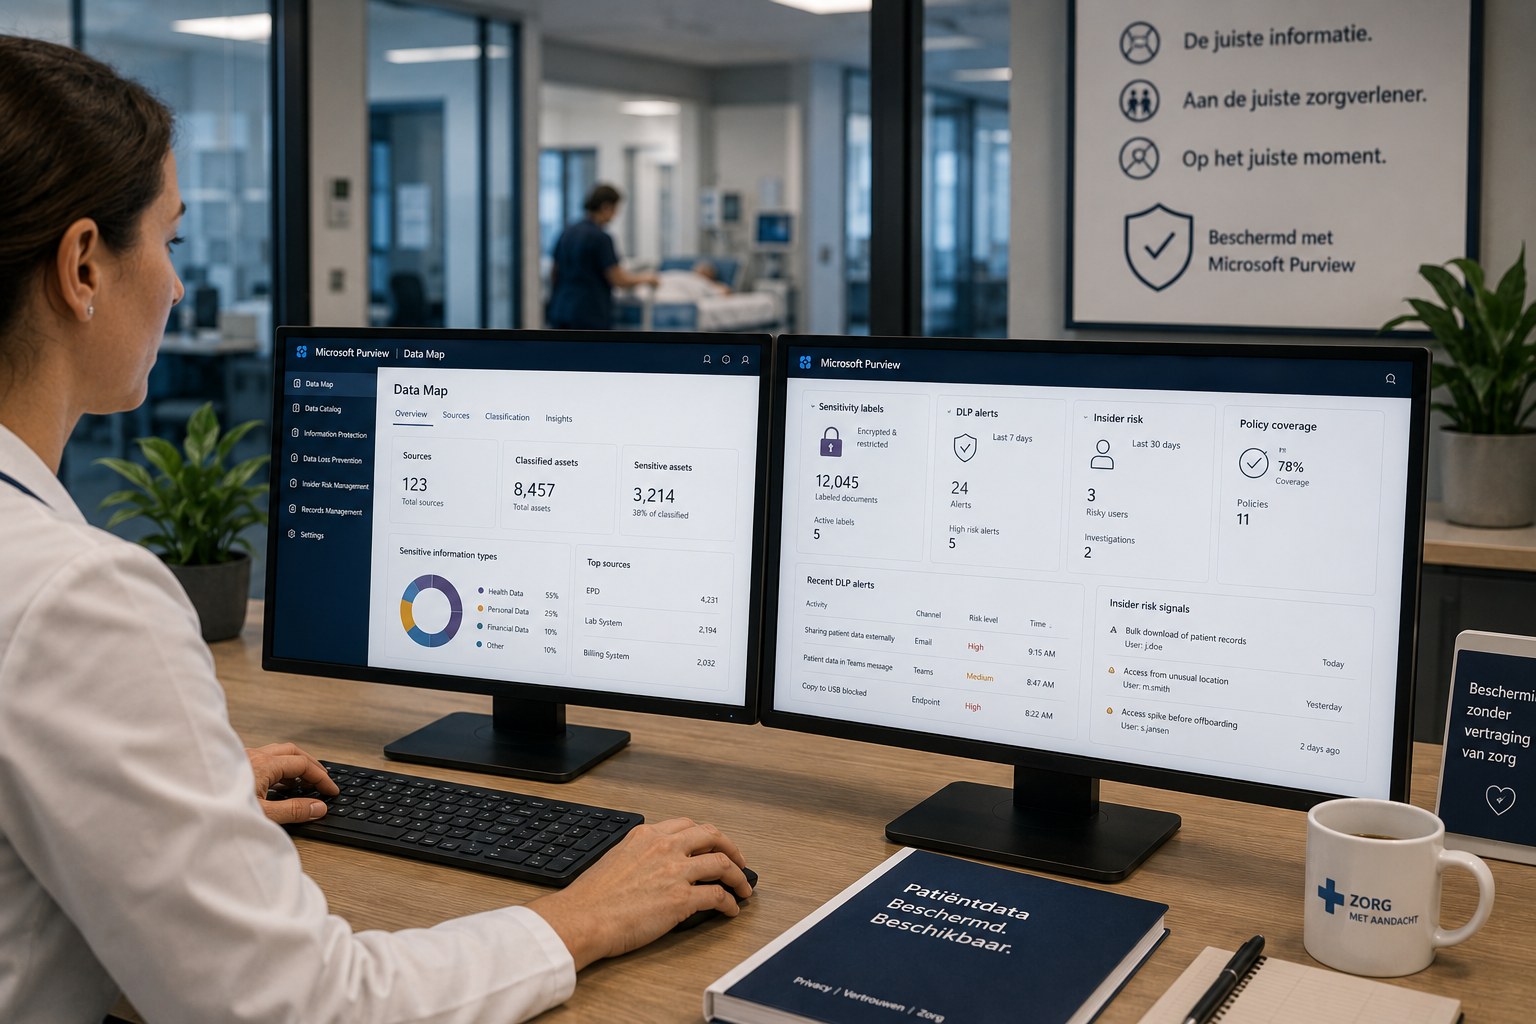
At a healthcare organization, patient data sat scattered across the EHR, lab systems and billing systems. Who exactly had access to special category health data could no longer be reconstructed, and there was no visibility into where that data went via mail or Teams. A GDPR audit exposed the problem: classification was missing, and so was protection.
Architecture
Microsoft Purview Data Map scans the source systems and automatically classifies content by sensitive information type, with health data as its own category. Based on that classification, patient data receives a sensitivity label with encryption and access restriction, carrying through into Outlook, Teams and SharePoint. DLP policy watches mail, Teams and endpoints, and blocks or warns the moment labeled patient data threatens to leave the managed network. Insider Risk Management flags anomalous behavior, such as bulk downloads of patient records shortly before an employee's departure.
Why this choice
The organization did not need a separate classification tool next to a separate DLP product: the gain was one policy layer carrying both the label and the block. Because the label travels with the document, protection stays intact even if a file accidentally ends up outside the intended channel.
Alternatives
A purely email-focused DLP solution protected the most common leak channel, but left Teams, endpoints and SharePoint open. For special category data under GDPR oversight, that was too large a residual risk.
Trade-offs
- Pattern-based classification produces false positives early on; those need tuning before DLP moves to block mode.
- Insider Risk Management requires careful scoping: monitoring too broadly feels like distrust, too narrow misses the risk.
- Auto-labeling scales protection but still needs review for edge cases where classification gets it wrong.
Microsoft products
Microsoft Purview (Data Map, Information Protection, Data Loss Prevention, Insider Risk Management), Microsoft Entra ID, Microsoft 365 (Exchange, Teams, SharePoint).
Best practices
- Start classification with the most sensitive data source (here, the EHR), not the easiest one.
- Run DLP in test mode with policy tips first, and only move to blocking once false positives are under control.
- Tie Insider Risk signals to concrete scenarios, such as an employee's departure or an unusual bulk download, instead of generic thresholds.
Lessons learned
The biggest resistance came from clinicians who experienced the label as an extra click. Auto-labeling based on classification largely solved that: the vast majority of patient data got the correct label without manual action, and the remaining manual labels only applied to edge cases.
Architecture at a glance
Click a component for details
EHR, lab, billing
Patient data sits scattered across multiple source systems.
The label travels with the document, so protection stays intact even outside the intended channel.
Related content
Related how-tos
Related best practices