
|
Best PracticeLevel: Advanced

Information Protection at enterprise scale

Implement sensitivity labels, encryption, auto-labeling, and protection policies that work consistently across Microsoft 365, Copilot, Teams, SharePoint, and Exchange.

TechExplained 1 min readPublished: 2 May 2026Last updated: 2 May 2026
#sensitivity labels#encryption#auto-labeling#information protection
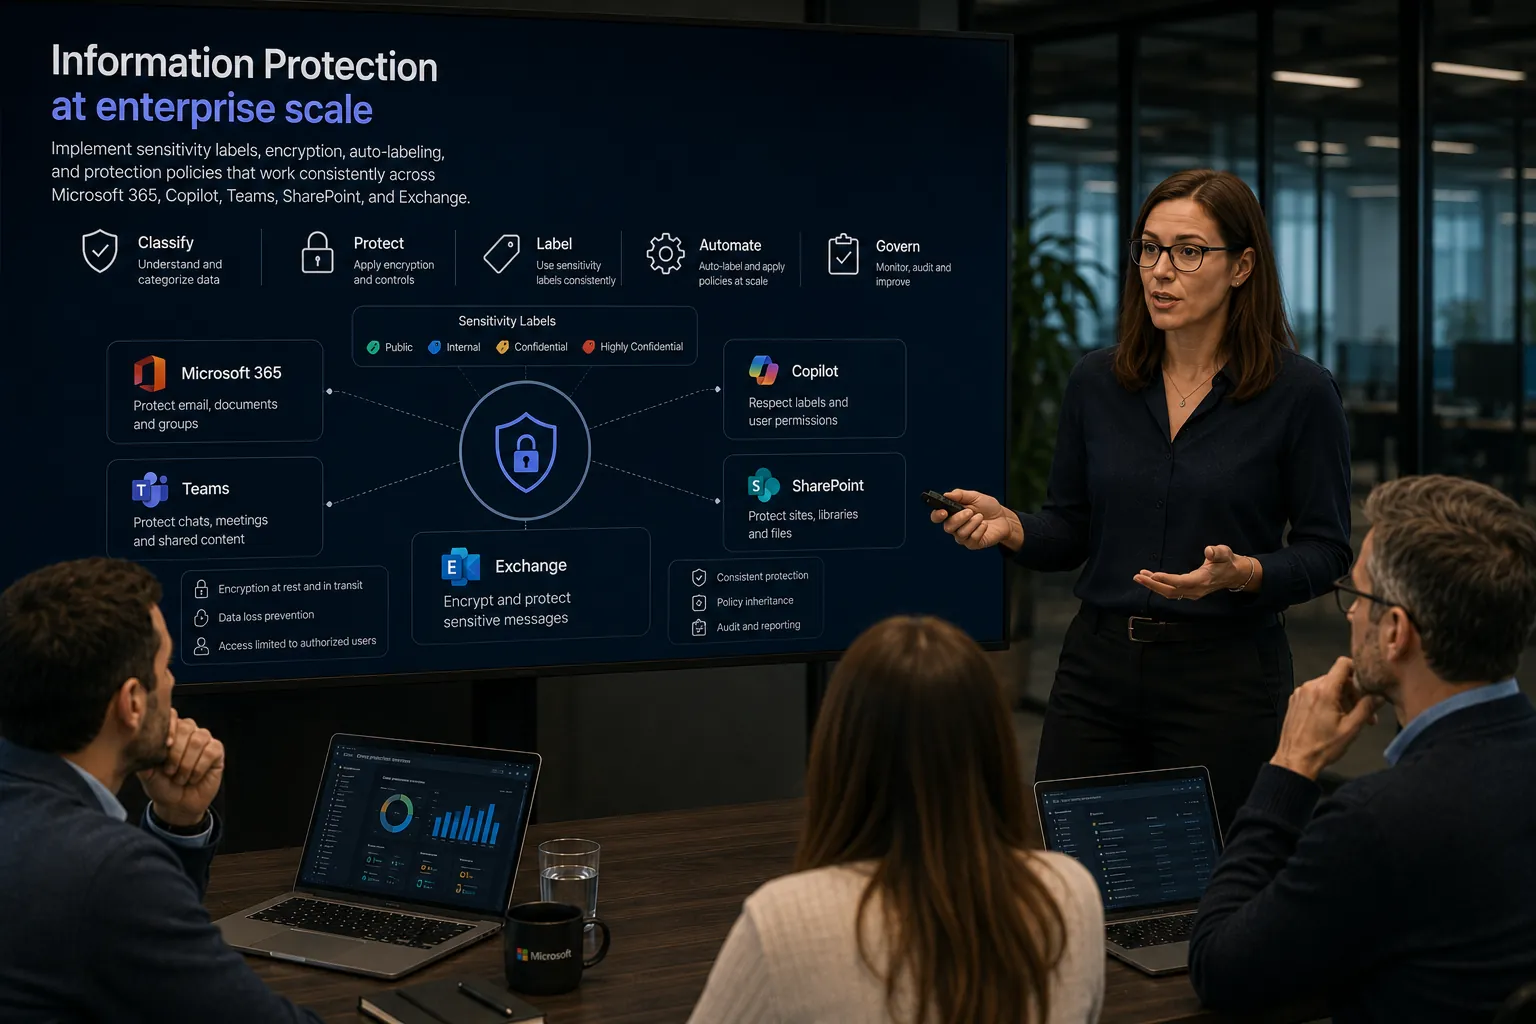
Architect walking a team through information protection at enterprise scale with sensitivity labels, encryption and protection policies across Microsoft 365, Copilot, Teams, SharePoint and Exchange, on screen.
01

Keep the label taxonomy small

The biggest mistake in Information Protection is a taxonomy of twenty labels nobody remembers. Limit yourself to a handful of levels everyone can explain, such as Public, Internal, Confidential, and Highly Confidential. A label set that fits on a sticky note gets used; a label set that needs a training gets ignored.

02

Auto-labeling beats manual discipline

Do not count on users to label every document by hand. Use auto-labeling based on content (credit card numbers, customer data, contract terms) so sensitive information gets the right protection even without human action. Test the policy in simulation mode first, because an overly aggressive rule labels half the organization Confidential and breaks workflows.

03

Encryption is the teeth behind the label

A label with no attached protection is little more than a sticker. Decide per level which encryption and usage rights apply: who may open, copy, print, or forward. That way the protection travels with the file, even outside the organization.

04

Consistency across workloads decides success

Labels must mean the same thing in Microsoft 365, Teams, SharePoint, and Exchange. A Confidential document that suddenly becomes freely shareable through Teams undermines the whole model. Configure the policy centrally and check that every workload respects it.

05

Validate what Copilot does with sensitive data

Microsoft 365 Copilot honors sensitivity labels and usage rights, but only when they are applied correctly. Explicitly test that Copilot does not summarize Highly Confidential content for users without rights. Information Protection and Copilot governance are two sides of the same coin.

The process at a glance

Click a step for its key decision

Summary

Keep the label taxonomy small

The biggest mistake in Information Protection is a taxonomy of twenty labels nobody remembers. Limit yourself to a handful of levels everyone can explain, such as Public, Internal, Confidential, and Highly Confidential. A label set that fits on a sticky note gets used; a label set that needs a training gets ignored.

Production Readiness Checklist

Before you go live, verify these production recommendations.

  • Label taxonomy kept to a handful of levels
  • Auto-labeling tested before rollout
  • Encryption and usage rights set per label
  • Labels consistent across Microsoft 365, Teams, SharePoint, and Exchange
  • Copilot behavior validated per sensitivity
  • Exceptions and overrides logged and reviewed
Information Protection at enterprise scale | TechExplained