
 Technology: Microsoft Purview
Manufacturing: protecting intellectual property with Microsoft Purview
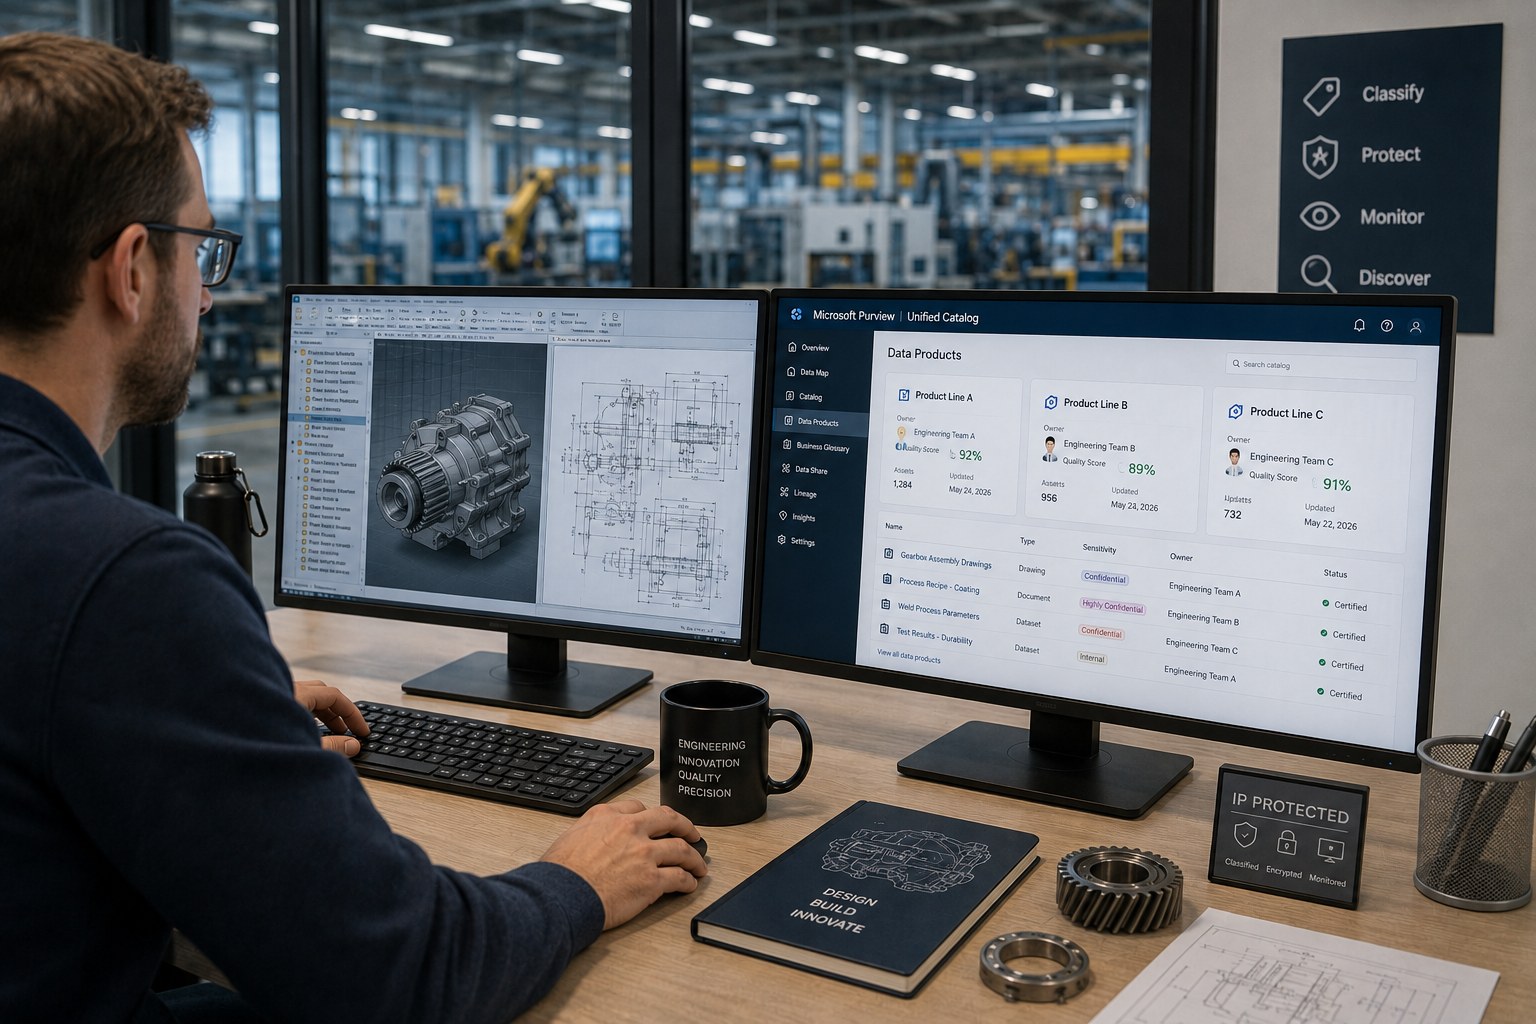
A manufacturer protects drawings, recipes and process data with classification, encrypted labels and Endpoint DLP, while making engineering data findable through the Unified Catalog at the same time.
Business challenge
A manufacturer with valuable drawings, recipes and process data had no visibility into where that intellectual property was going: engineering files circulated to suppliers via email and USB drives without any control. At the same time, engineers complained they could not find existing drawings from earlier projects.
Architecture
The Data Map scans engineering systems and PLM environments and classifies files by content and context. Sensitive IP files receive a sensitivity label with encryption, so the file can only be opened by authorized users, even after it has left the corporate network. Endpoint DLP watches copy actions to USB devices and blocks or warns on unprotected IP files. At the same time, those same files are included in Data Products within the Unified Catalog, with an owner per product line, so engineers find existing work instead of redesigning it.
Why this choice
Protection and findability had long been treated as competing goals: tightening security seemed to mean worse searchability. Because labeling and cataloging run on the same classification base, the organization did not have to choose: an encrypted file stays findable in the catalog for those entitled to it.
Alternatives
A separate PLM access control without Purview integration restricted access within the PLM system itself, but left a file fully unprotected once it had been exported, to email or USB. For IP that by nature also circulates outside the PLM system, toward suppliers, that was a gap.
Trade-offs
- File-level encryption can complicate collaboration with external partners if they do not share the same identity infrastructure.
- Endpoint DLP on aging shop-floor devices required additional device management before the policy could apply everywhere.
- Classification of CAD files and process data is less mature than classification of text documents; manual validation was still needed for specialist file formats.
Microsoft products
Microsoft Purview (Data Map, Information Protection, Data Loss Prevention, Unified Catalog), Microsoft Entra ID.
Best practices
- Start with the most valuable IP category, for example recipes, instead of classifying everything at once.
- Tie label policy to concrete export scenarios: email to external domains, USB, cloud storage outside the tenant.
- Give Data Products an owner per product line, so findability does not decay once the initial project wraps up.
Lessons learned
File-level encryption turned out to be a stronger safeguard than access control alone: even after a file was accidentally shared broadly, its content stayed inaccessible to unauthorized users. The biggest resistance came from engineers who expected extra steps; auto-labeling based on classification kept that burden low.
Architecture at a glance
Click a component for details
Engineering / PLM
Drawings, recipes and process data as source.
An encrypted file stays findable in the catalog for those entitled to it, protection and findability need not be competing goals.
Related content
Related how-tos
Related best practices