
|
Best PracticeLevel: Intermediate

Rolling out Microsoft 365 Copilot: remediating oversharing and governing agents

Why Copilot does not create access but inherits existing permissions, and how to remediate oversharing, pick the right agent building block, and govern agents before broad adoption.

TechExplained 3 min readPublished: 26 July 2026Last updated: 26 July 2026
#copilot#oversharing#agent governance#sharepoint
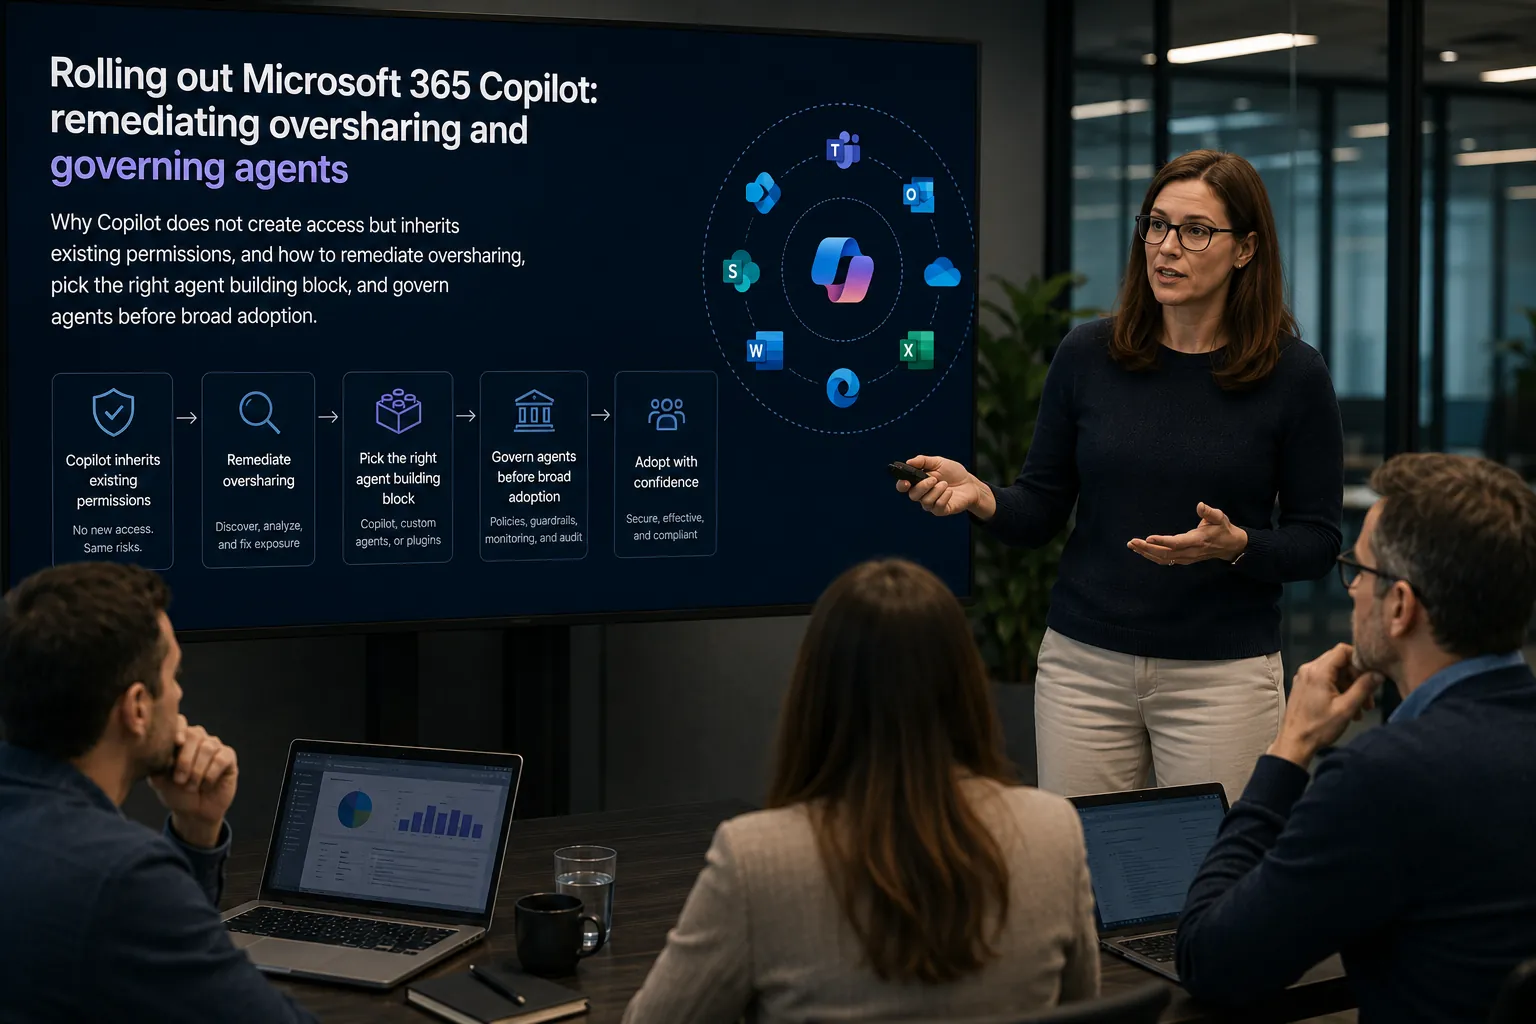
Architect walking a team through rolling out Microsoft 365 Copilot: remediating oversharing and governing agents, on screen.
01

Copilot does not create access, it inherits existing permissions

The most underestimated architecture decision in a Copilot rollout is not about Copilot itself, but about the permissions already in place. Copilot only shows content the user already has access to, security trimming ensures that, but it also means every overly broad site or folder suddenly becomes findable through a simple question instead of an accidental search. Oversharing is therefore not a risk Copilot introduces, it is a risk that already existed and that Copilot makes visible for the first time.

02

Remediate oversharing before you go live, not after

Use Restricted Content Discovery (RCD) to temporarily limit the grounding scope to sites with correct permissions, and use SharePoint Advanced Management to identify and clean up overly broad sites. Do this before rollout, not in reaction to an incident. An organization that remediates first and expands afterward sees almost no reports of unwanted visible content; an organization that rolls out broadly and remediates afterward has to fix permissions while users are already actively searching.

Do bear in mind that this tooling is about SharePoint. Since the Copilot release of 25 August 2026, private Viva Engage communities and events are a grounding source as well, and those never come up in an RCD remediation. The effective boundary there is membership of the community, and in most organizations that list was last reviewed years ago. So take those member lists into the same remediation, and treat them as an authorization decision rather than a social list.

03

Let classification carry the policy, not loose per-channel rules

Sensitivity labels and Purview DLP carry through into every Copilot answer: a label that protects a document in SharePoint also protects it when Copilot cites it. Set up labels and DLP as the foundation under the rollout, not as an afterthought. A generic, overly coarse label scheme gets ignored; a scheme that matches how employees already think about their data actually gets applied.

04

Choose deliberately between out-of-the-box Copilot and an agent

Not every need calls for an agent. Out-of-the-box Copilot in the Office apps and Copilot Chat is enough for generic productivity. A declarative agent adds its own knowledge and instructions without code, and is the right first step once a team repeatedly asks the same question about its own content. Microsoft recognizes two agent types: declarative agents and custom engine agents. Copilot Studio is not a third type but builds declarative agents with low-code actions on top, useful once the Agent Builder falls short. A custom engine agent on Microsoft Foundry, published to Copilot or Teams, is only needed for complex orchestration or model choices beyond what the Copilot stack offers. Start at the simplest layer that solves the problem, not the heaviest.

05

Govern agents with the same discipline as the base rollout

Agents without governance lead to sprawl: unclear ownership, uncontrolled actions, and nobody knowing which agent is still in use. The Copilot Control System is the central place for approving, owning and monitoring agents, alongside rollout and adoption reporting for Copilot itself. Treat publishing a new agent as a release, with an owner and a review step, not as a free action anyone can take without oversight.

06

The most common mistake: rolling out without remediation

The biggest, most common mistake is switching on Copilot organization-wide before oversharing is resolved, assuming the problem can be fixed later. In practice it is the opposite: once users start actively searching, the momentum to fix permissions is gone, and every report of unwanted visible content undermines trust in the whole initiative. Remediate first, then roll out.

The process at a glance

Click a step for its key decision

Summary

Copilot does not create access, it inherits existing permissions

The most underestimated architecture decision in a Copilot rollout is not about Copilot itself, but about the permissions already in place. Copilot only shows content the user already has access to, security trimming ensures that, but it also means every overly broad site or folder suddenly becomes findable through a simple question instead of an accidental search. Oversharing is therefore not a risk Copilot introduces, it is a risk that already existed and that Copilot makes visible for the first time.

Production Readiness Checklist

Before you go live, verify these production recommendations.

  • Oversharing remediated with Restricted Content Discovery (RCD) and SharePoint Advanced Management before broad rollout
  • Sensitivity labels and Purview DLP set up and working inside Copilot
  • Grounding scope (sites, connectors) deliberately defined, not everything by default
  • Membership of private Viva Engage communities reviewed, because those are a grounding source too since August 2026
  • Agent building block (declarative, Copilot Studio, Foundry) chosen by complexity, not the heaviest by default
  • Agent governance (approval, ownership, monitoring) set up through the Copilot Control System
  • Audit of Copilot interactions set up before broad adoption
Microsoft 365 Copilot: oversharing and agent governance