
How to set up Microsoft Purview data governance
From scanning your data estate to sensitivity labels, DLP, governance domains and compliance: the order and the choices that actually matter.
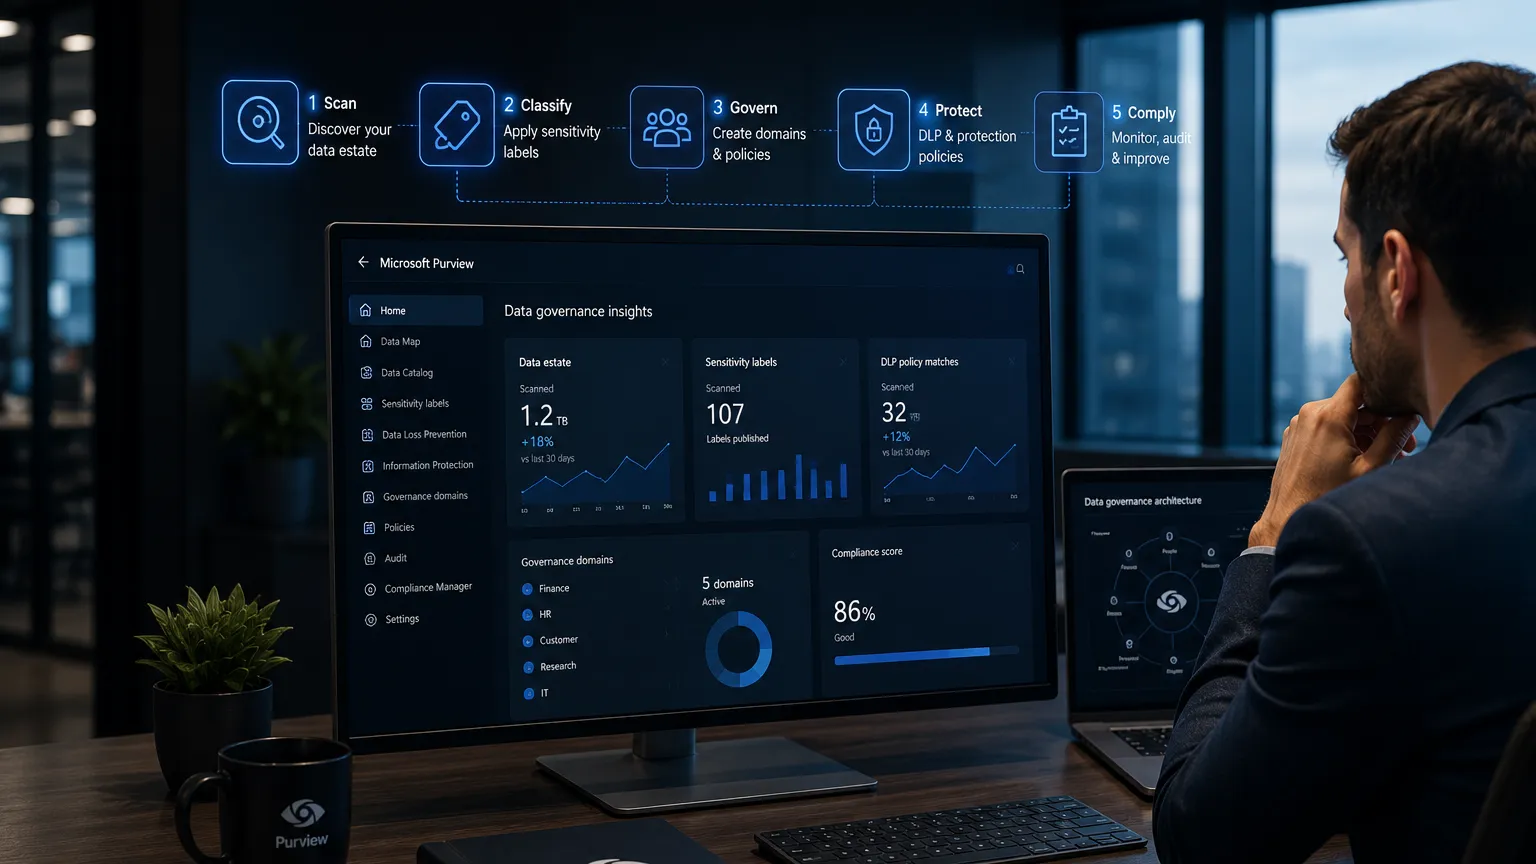
- 01
Start with your data estate, not with labels
Before you label or block anything, you need to know what data you have and where. Register your sources in the Microsoft Purview Data Map and scan them, so the Unified Catalog gives you an up-to-date view of your data estate. Without that inventory you are labeling blind.
Decisionwhich sources do you scan first? Start with the systems that hold the most sensitive data and the most sharing, not the easiest ones. - 02
Design a sensitivity label taxonomy people understand
Information Protection lives or dies by a short, understandable set of labels (for example Public, Internal, Confidential and Highly Confidential). Too many labels lead to wrong choices and label fatigue. Publish them through label policies and turn on auto-labeling based on sensitive information types.
Decisionhow many labels? Keep it under five top-level labels; sublabels only when a concrete rule requires them. - 03
Roll out Data Loss Prevention in a targeted, phased way
Define DLP policies based on labels and locations (SharePoint, OneDrive, Teams, endpoints). Always start in monitor or warning mode, measure the false positives, and only then move to blocking. A DLP policy that blocks hard from day one gets switched off within a week.
Decisionblock or warn? Start with warn plus override-with-reason, and block only the scenarios that demonstrably must not happen. - 04
Set up governance domains and data products
In the Unified Catalog you manage governance per domain: assign owners, publish data products and define data quality rules. Governance without ownership stalls; a domain without an owner is a catalog nobody maintains.
Decisionper domain or centralized? Choose federated governance with central policies and decentralized owners, unless your organization is too small for domains. - 05
Compliance, audit and risk
Use Compliance Manager to make your compliance posture measurable, Audit for traceability and eDiscovery for investigations. Insider Risk Management flags risky behavior around sensitive data. Do not turn all of these on at once; pick the risks that weigh heaviest for your sector.
Decisionwhich risks first? Start with the risk that has the highest impact and the clearest regulation, not the full package. - 06
Data lifecycle and retention
Use retention labels and policies to define how long data must be kept and when it may go. Information governance prevents both deleting too early (a compliance risk) and keeping forever (cost and oversharing).
Decisionkeep or delete as the default? Choose deliberately per data category; an organization-wide "keep everything" is rarely the cheapest or safest choice. - 07
Measure, clean up and repeat
Use Data Estate Insights to see where sensitive data sits, where oversharing appears and whether labels are correct. Governance is a product, not a project: clean up oversharing, refine labels and repeat the scan periodically.
The process at a glance
Click a step for its key decision
Start with your data estate, not with labels
which sources do you scan first? Start with the systems that hold the most sensitive data and the most sharing, not the easiest ones.
Read next
Related use cases
Related best practices